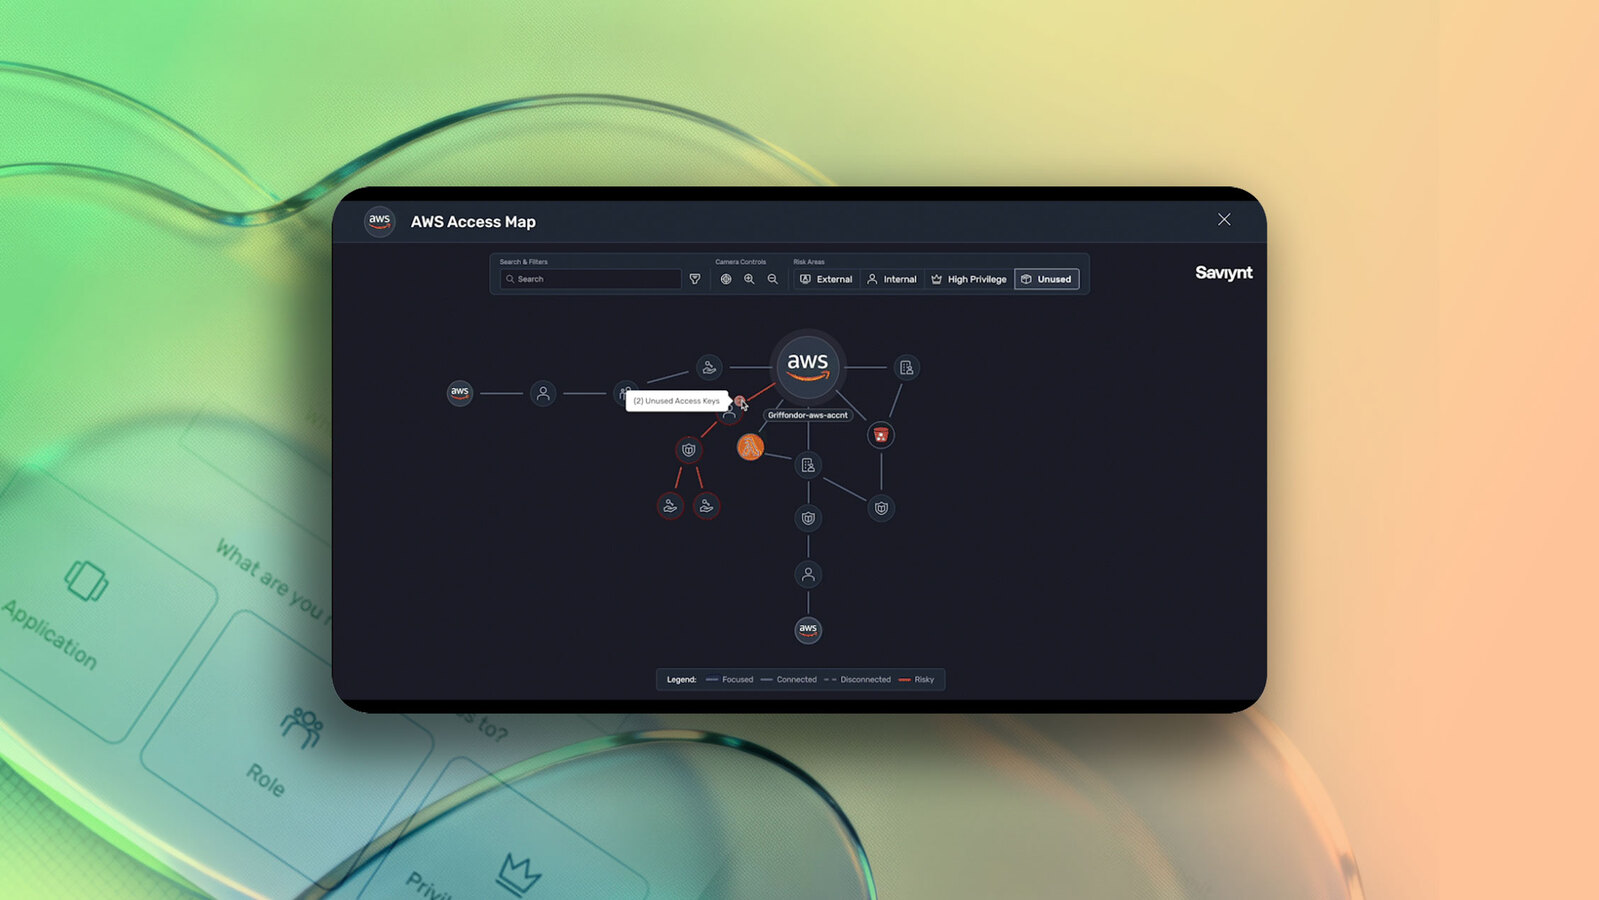
An employee leaves your company on a Friday; by Monday, their AWS Identity and Access Management (IAM) role is still active, assigned to three production accounts – yet no one flagged it. This isn't a hypothetical; it's the reality of most enterprise AWS environments today. And it's exactly the kind of access that may not surface in an audit, or leaves your environment with a compliance gap.
The root cause is complexity, not carelessness. As organizations scale from dozens to thousands of AWS accounts, access accumulates faster than it can be governed. AWS IAM Identity Center has provided a centralized way to manage workforce access across accounts through Permission Sets. Now, with the introduction of AWS IAM Account access manager (AAM), organizations can assign existing IAM roles directly to Identity Center users and groups, without converting those roles into Permission Sets first.
Saviynt is proud to be an AWS launch partner for AAM, extending our industry-leading Identity Governance and Administration (IGA) platform to govern these new direct role assignments alongside existing Permission Set governance, all from a single pane of glass. In this post, you will learn how Saviynt extends its IGA platform to govern these direct role assignments, so you can see, request, certify, and revoke every AWS identity from one place.
Governing what you can’t see
Today’s enterprise AWS environments contain a sprawling mix of access mechanisms:
- Permission Sets managed centrally via IAM Identity Center
- Custom IAM roles created by application teams in individual accounts
- Legacy IAM roles inherited from acquisitions, migrations, or early cloud experiments
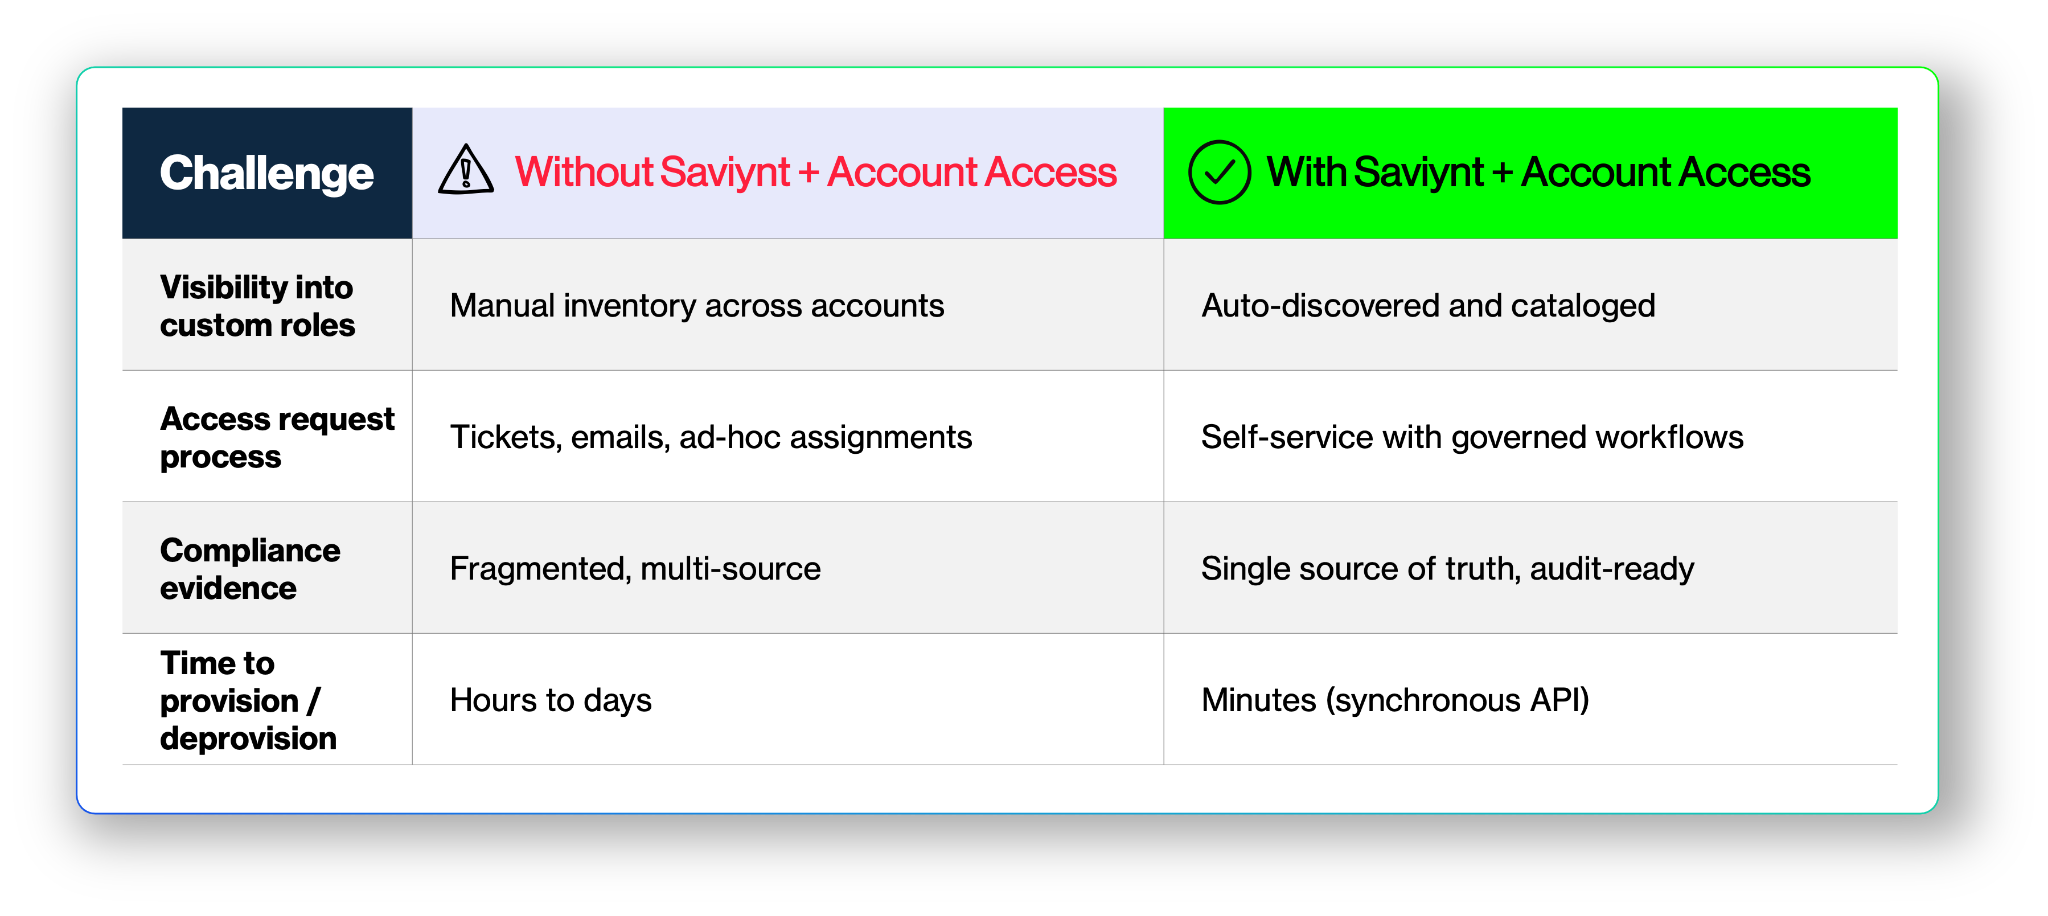
While Permission Sets offer a structured, auditable approach to access, many organizations also rely on hundreds of custom IAM roles that pre-date their Identity Center deployment. These roles often fall outside governance workflows, creating gaps in governance visibility in three common ways:
- Over-provisioned identities where users accumulate role access they no longer need
- Orphaned assignments where users are deleted but access records persist, creating phantom entitlements
- Compliance gaps where teams must reconcile multiple sources of truth when auditors ask "who can access what?"
Until now, governing these custom roles required manual effort and disconnected tooling. AAM, combined with Saviynt’s governance integration changes that.
The solution: unified governance with Saviynt + AAM
Governing AWS access shouldn't require a different tool for every type of assignment — or a team of specialists to reconcile them all. It should let you answer one question with confidence: who can access what, and is that access still appropriate?
Saviynt's integration with AAM delivers full identity governance lifecycle capabilities to existing IAM roles and their assignments. By extending our Unified AWS Connector, Saviynt enables organizations to manage both Permission Sets and AAM IAM roles through the same governance workflows they already know and trust.
No new workflows to learn. No parallel systems to maintain. One place to see, manage, and certify all AWS access; whether it was created last week, three years ago, or years later, after the team that created it has moved on.
The result: your security and compliance teams finally get full access visibility and context. Your end users get a self-service experience that doesn't require opening a ticket and waiting. And your auditors get a single source of truth.
The integration delivers two key benefits: A unified console for all Identity Center Access and self-service IAM role requests and revocation.
A unified view for all Identity Center access
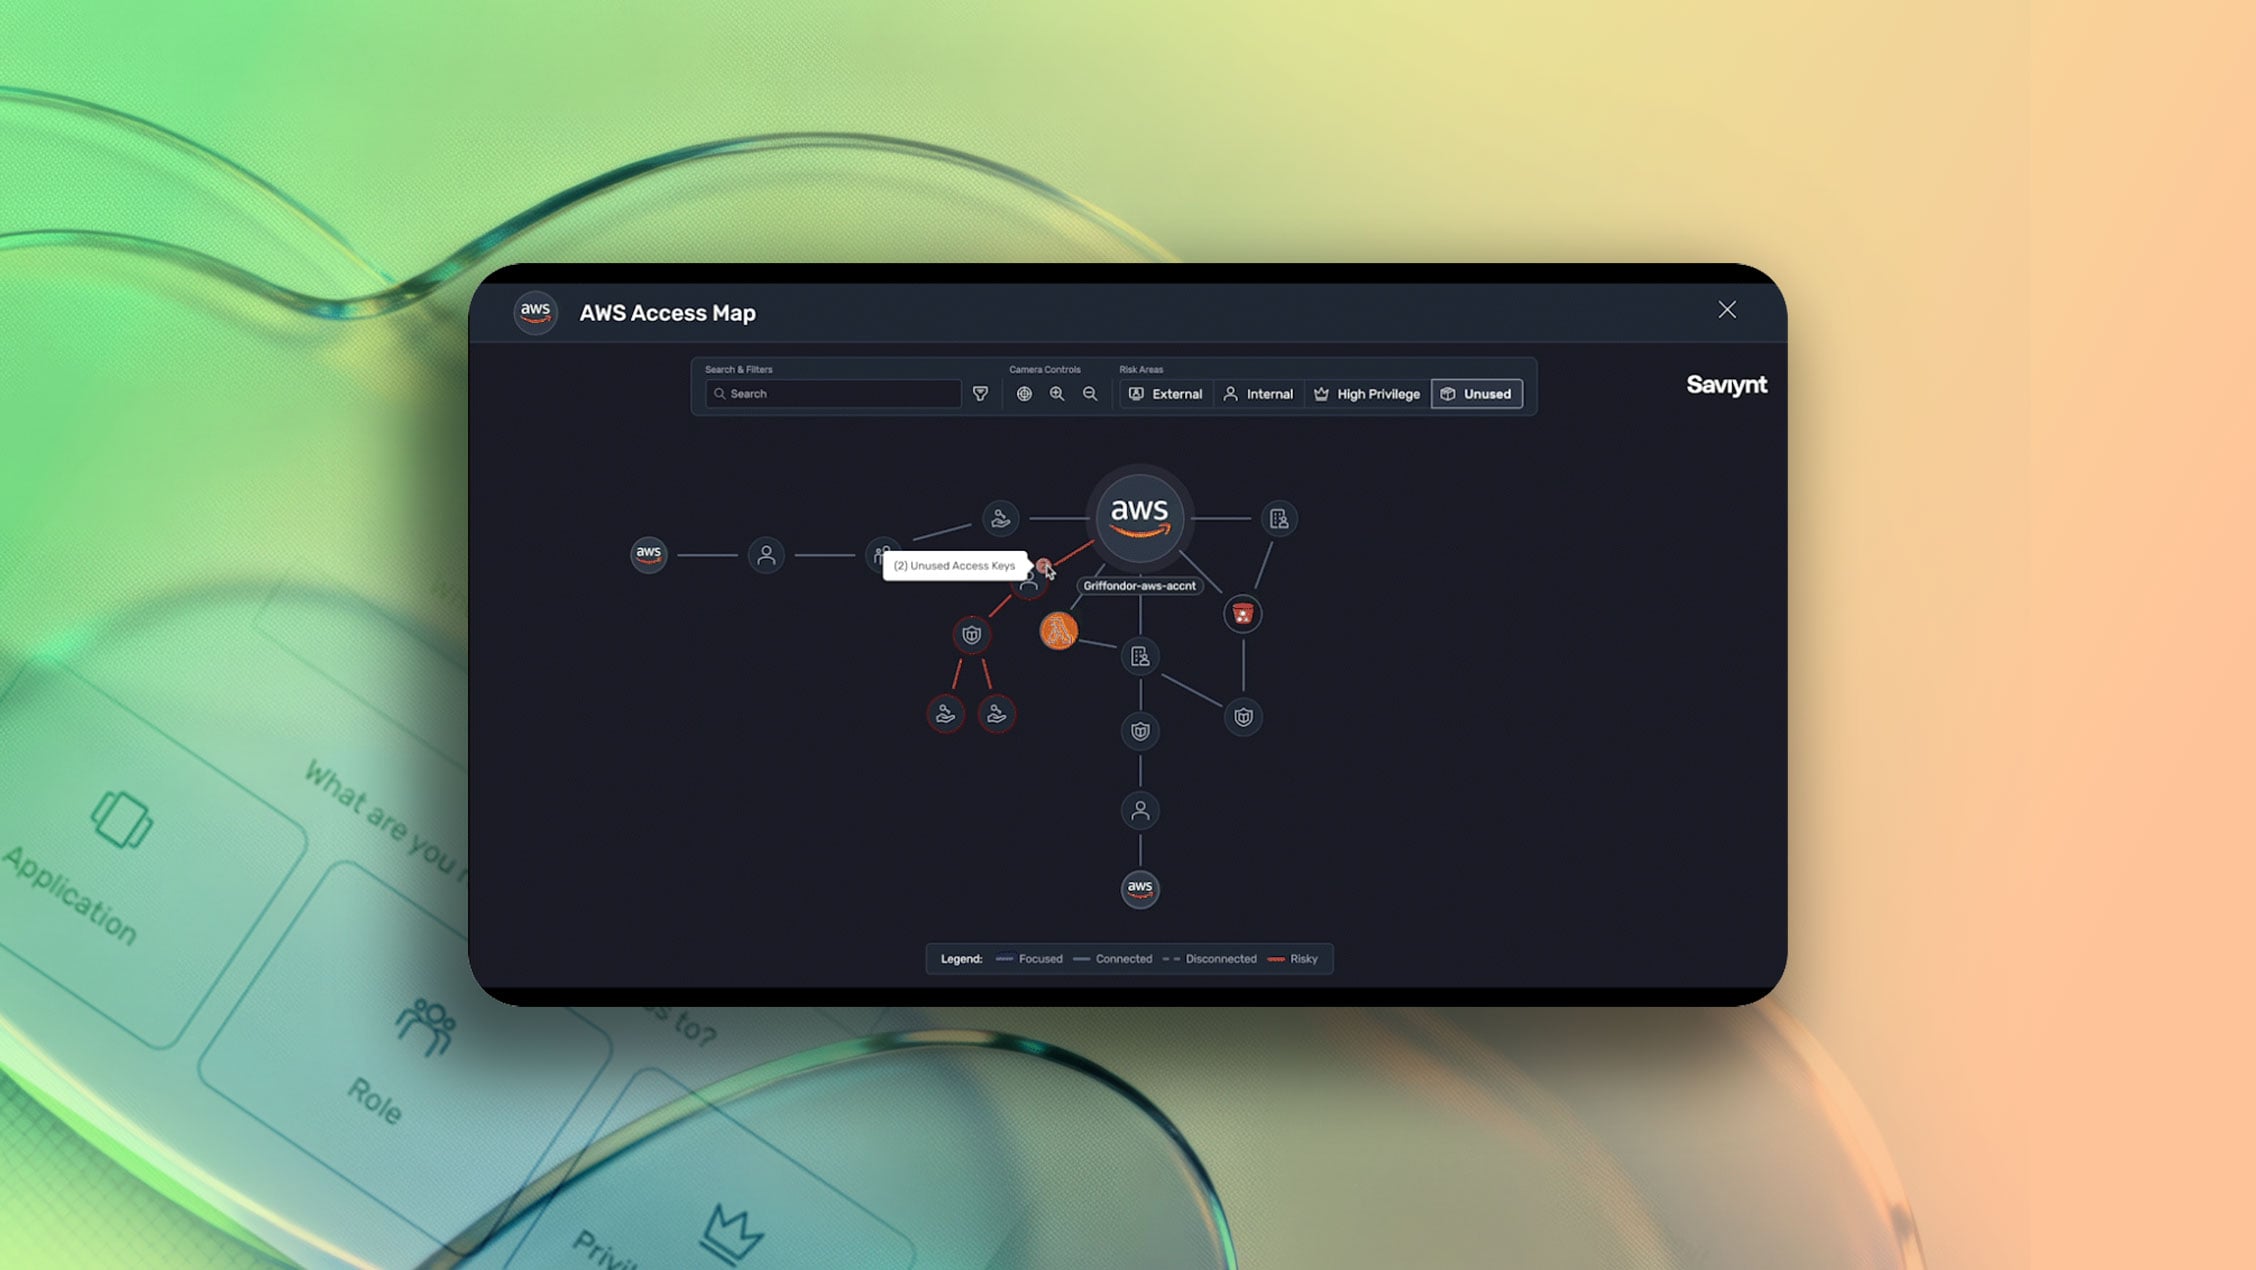
Provide complete visibility and governance across every type of Identity Center assignment; Permission Sets and IAM roles; in one unified console.
- Discover AAM role assignments across the organization automatically
- Correlate IAM Account access manager and permission set assignments to build a complete identity access map
- Certify all AWS access, templated and custom, through a single access review campaign
No more reconciling spreadsheets or running separate reports for different access mechanisms. One view. One workflow.
Self-service IAM role requests and revocation
Enable end-users to request and relinquish specific IAM roles through governed workflows to eliminate ad-hoc role assignments and shadow IT.
- Users browse a curated catalog of eligible IAM roles, organized by account and function
- Approval workflows route requests to the right business and technical owners
- Time-bound access ensures roles are granted with expiration policies, with no more standing permissions
- Single-action revocation lets users release access they no longer need, or managers can revoke at any time
This transforms IAM role access from an uncontrolled manual process into a governed, auditable experience that gives users self-service access while protecting the organization.
How It works: Architecture at a glance
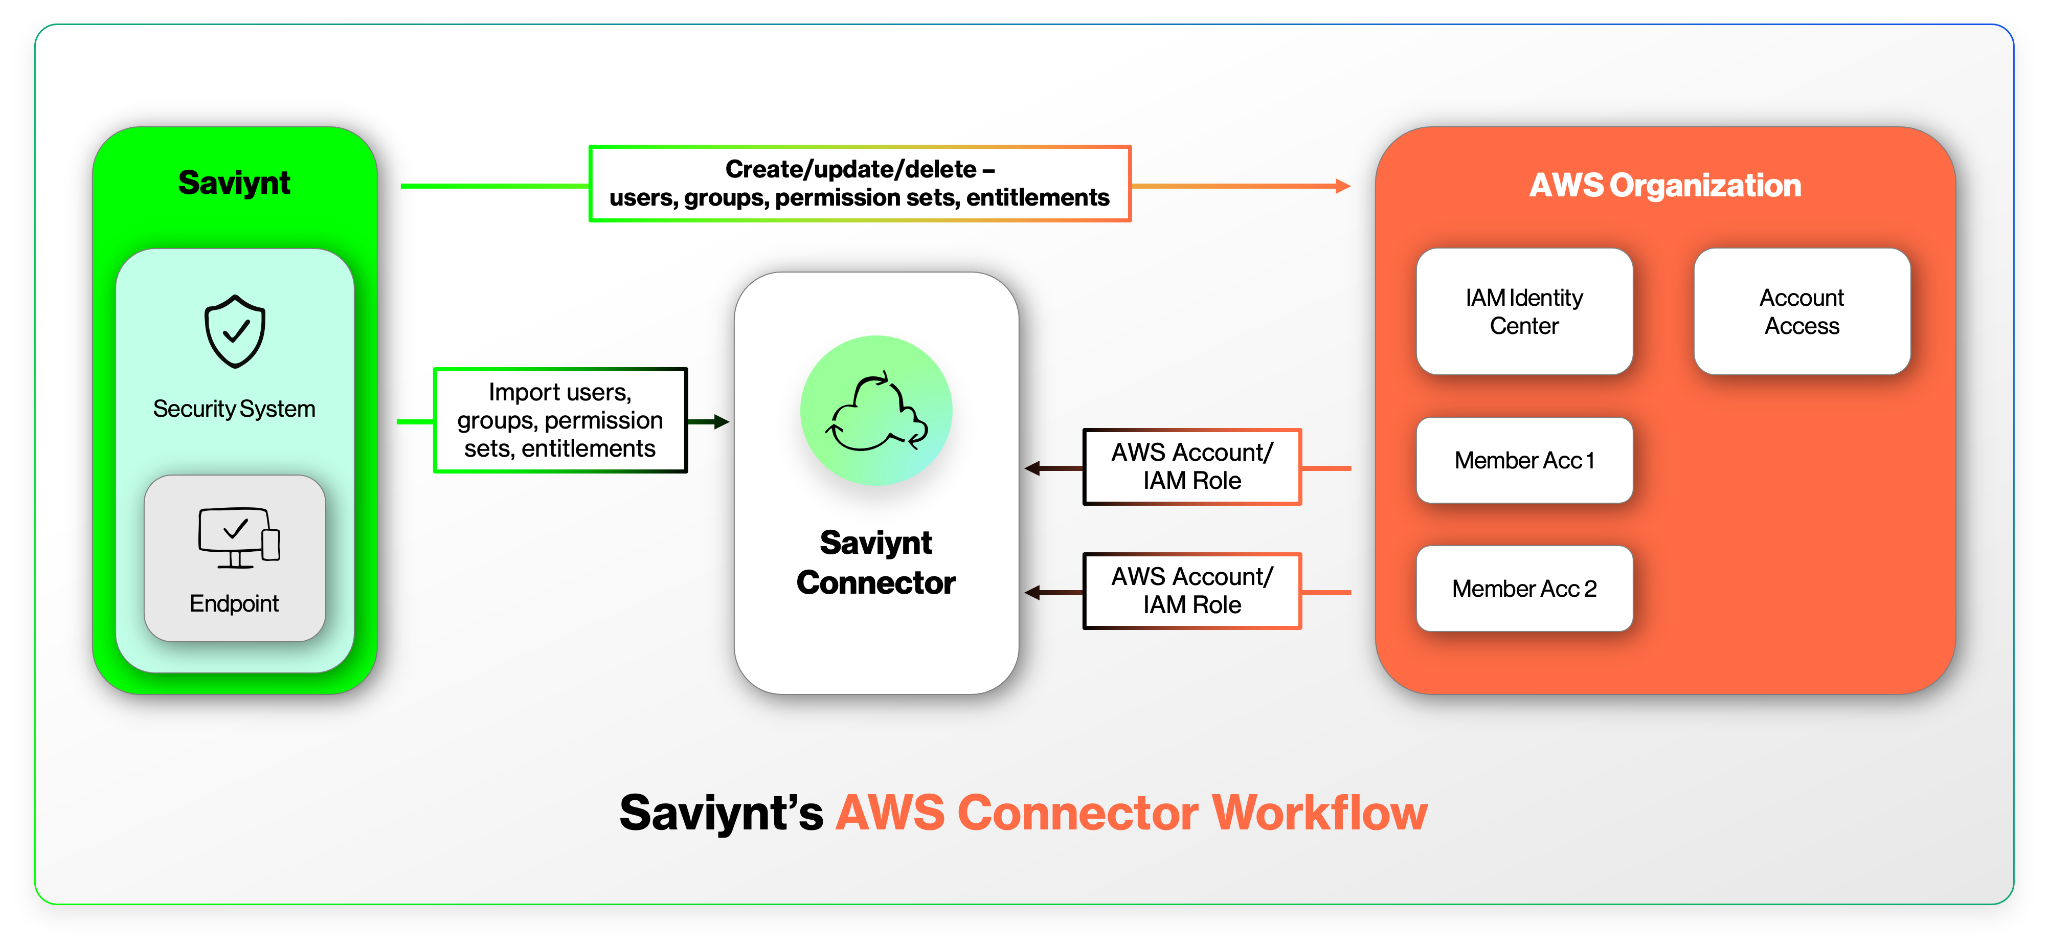
Saviynt's Unified AWS Connector extends to AAM, following a simple four-step flow:
- Discovery — Saviynt calls the AAM APIs from a hub account to discover role assignments across the organization
- Importing — Existing assignments are imported and correlated with Identity Center users and groups already managed in Saviynt
- Cataloging — Eligible IAM roles (those with the required trust policy) are identified and published as requestable entitlements
- Governance — Standard Saviynt workflows (request, approve, certify, revoke) apply to AAM roles with the same rigor as Permission Sets
Saviynt’s AWS Connector Workflow
Saviynt + AWS: A proven partnership
This launch builds on Saviynt's deep partnership with AWS, spanning multiple layers of collaboration. As an AWS Competency Partner for Security and a partner available directly through AWS Marketplace, Saviynt gives customers a trusted, streamlined path to procurement. That partnership is backed by existing integrations with AWS IAM Identity Center, AWS IAM Access Analyzer, AWS CloudTrail, and Amazon Bedrock, and extends into the agentic AI space through Saviynt’s MCP Server, launched as part of the AWS AI Agent and Tools Marketplace. Together, this collaboration ensures Saviynt and AWS customers benefit from day-one support for new AWS identity capabilities as they become available.
Getting Started
- If you’re an existing Saviynt customer — Contact your Customer Success Manager to enable the AAM extension in your Unified AWS Connector configuration
- If you’re new to Saviynt — Request a demo to see unified AWS governance in action at saviynt.com/request-a-demo
- If you want to enhance your access management capabilities right away - Head to Saviynt’s AWS Marketplace page.
Conclusion
By enabling direct IAM role assignment through Identity Center, AWS removes a longstanding gap while Saviynt ensures that gap doesn’t become a governance blind spot. To learn more, see AWS IAM Account access manager documentation and AWS IAM Identity Center.