AI adoption is no longer optional. It’s happening now across engineering, product, security, and business teams powered by AI‑native platforms like Claude and Kiro that are reshaping how work gets done.
Autonomous agents, embedded generative capabilities, and AI‑driven workflows are executing real business actions. And while the productivity gains are undeniable, so are the risks.
As organizations race to adopt AI, many are unintentionally creating their next major security and cost crisis with uncontrolled AI access, identity sprawl, and Shadow AI operating outside governance boundaries.
To address these issues and help organizations increase productivity without compromising security, we’re thrilled to announce that Saviynt IGA now integrates with Claude and Kiro, providing an identity-first way to govern AI without slowing innovation.
Why AI platforms can't be governed like traditional apps
AI platforms are fundamentally different from traditional enterprise software. They execute actions, process sensitive data autonomously, and introduce agentic capabilities that can operate independently of the user. Traditional IAM controls authorization, but they cannot keep up with what an AI agent is permitted to do, with whose data, or for how long.
Without centralized governance, organizations face:
- Sensitive data flowing into unmanaged AI models
- Excessive permissions granted “just to get started”
- No visibility into who has access (and why)
- Rising AI license costs with little accountability
This is exactly where Saviynt can help.
Saviynt IGA’s integration with Claude and Kiro extends identity governance to these leading AI platforms, delivering consistent control, visibility, and accountability across the entire lifecycle.

Key capabilities of the Saviynt IGA integration
The Saviynt IGA integration covers five core capabilities: day-one secure access, birthright provisioning for technical teams, self-service request workflows, least-privilege enforcement for AI agents, and license cost control through continuous certification.
Day-one secure access to AI
Saviynt IGA ensures Claude and Kiro are governed from the moment they’re introduced. No more unmanaged identities, less Shadow AI.
Birthright access for technical teams
Engineers, product managers, and AI specialists get immediate, role‑based access to the AI tools they need, automatically, without tickets, delays, or security trade-offs.
Self-service request for all other users
Any user can request specific AI capabilities through a centralized portal, where multi-level approvals can verify the business need and budget availability before access is granted.
Least privilege for AI agents
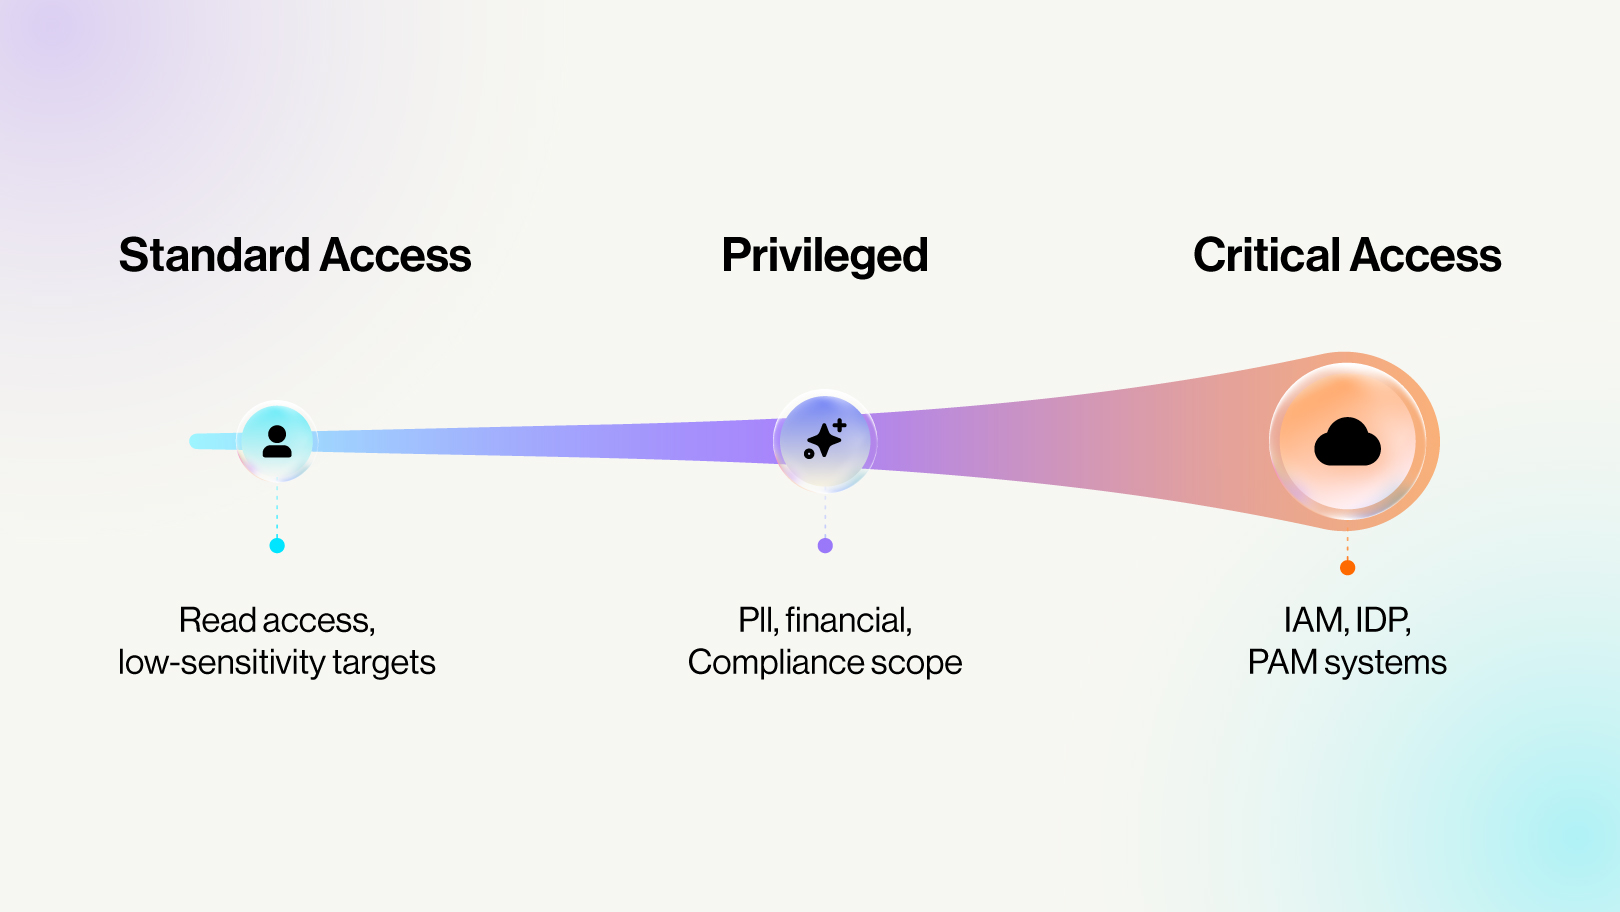
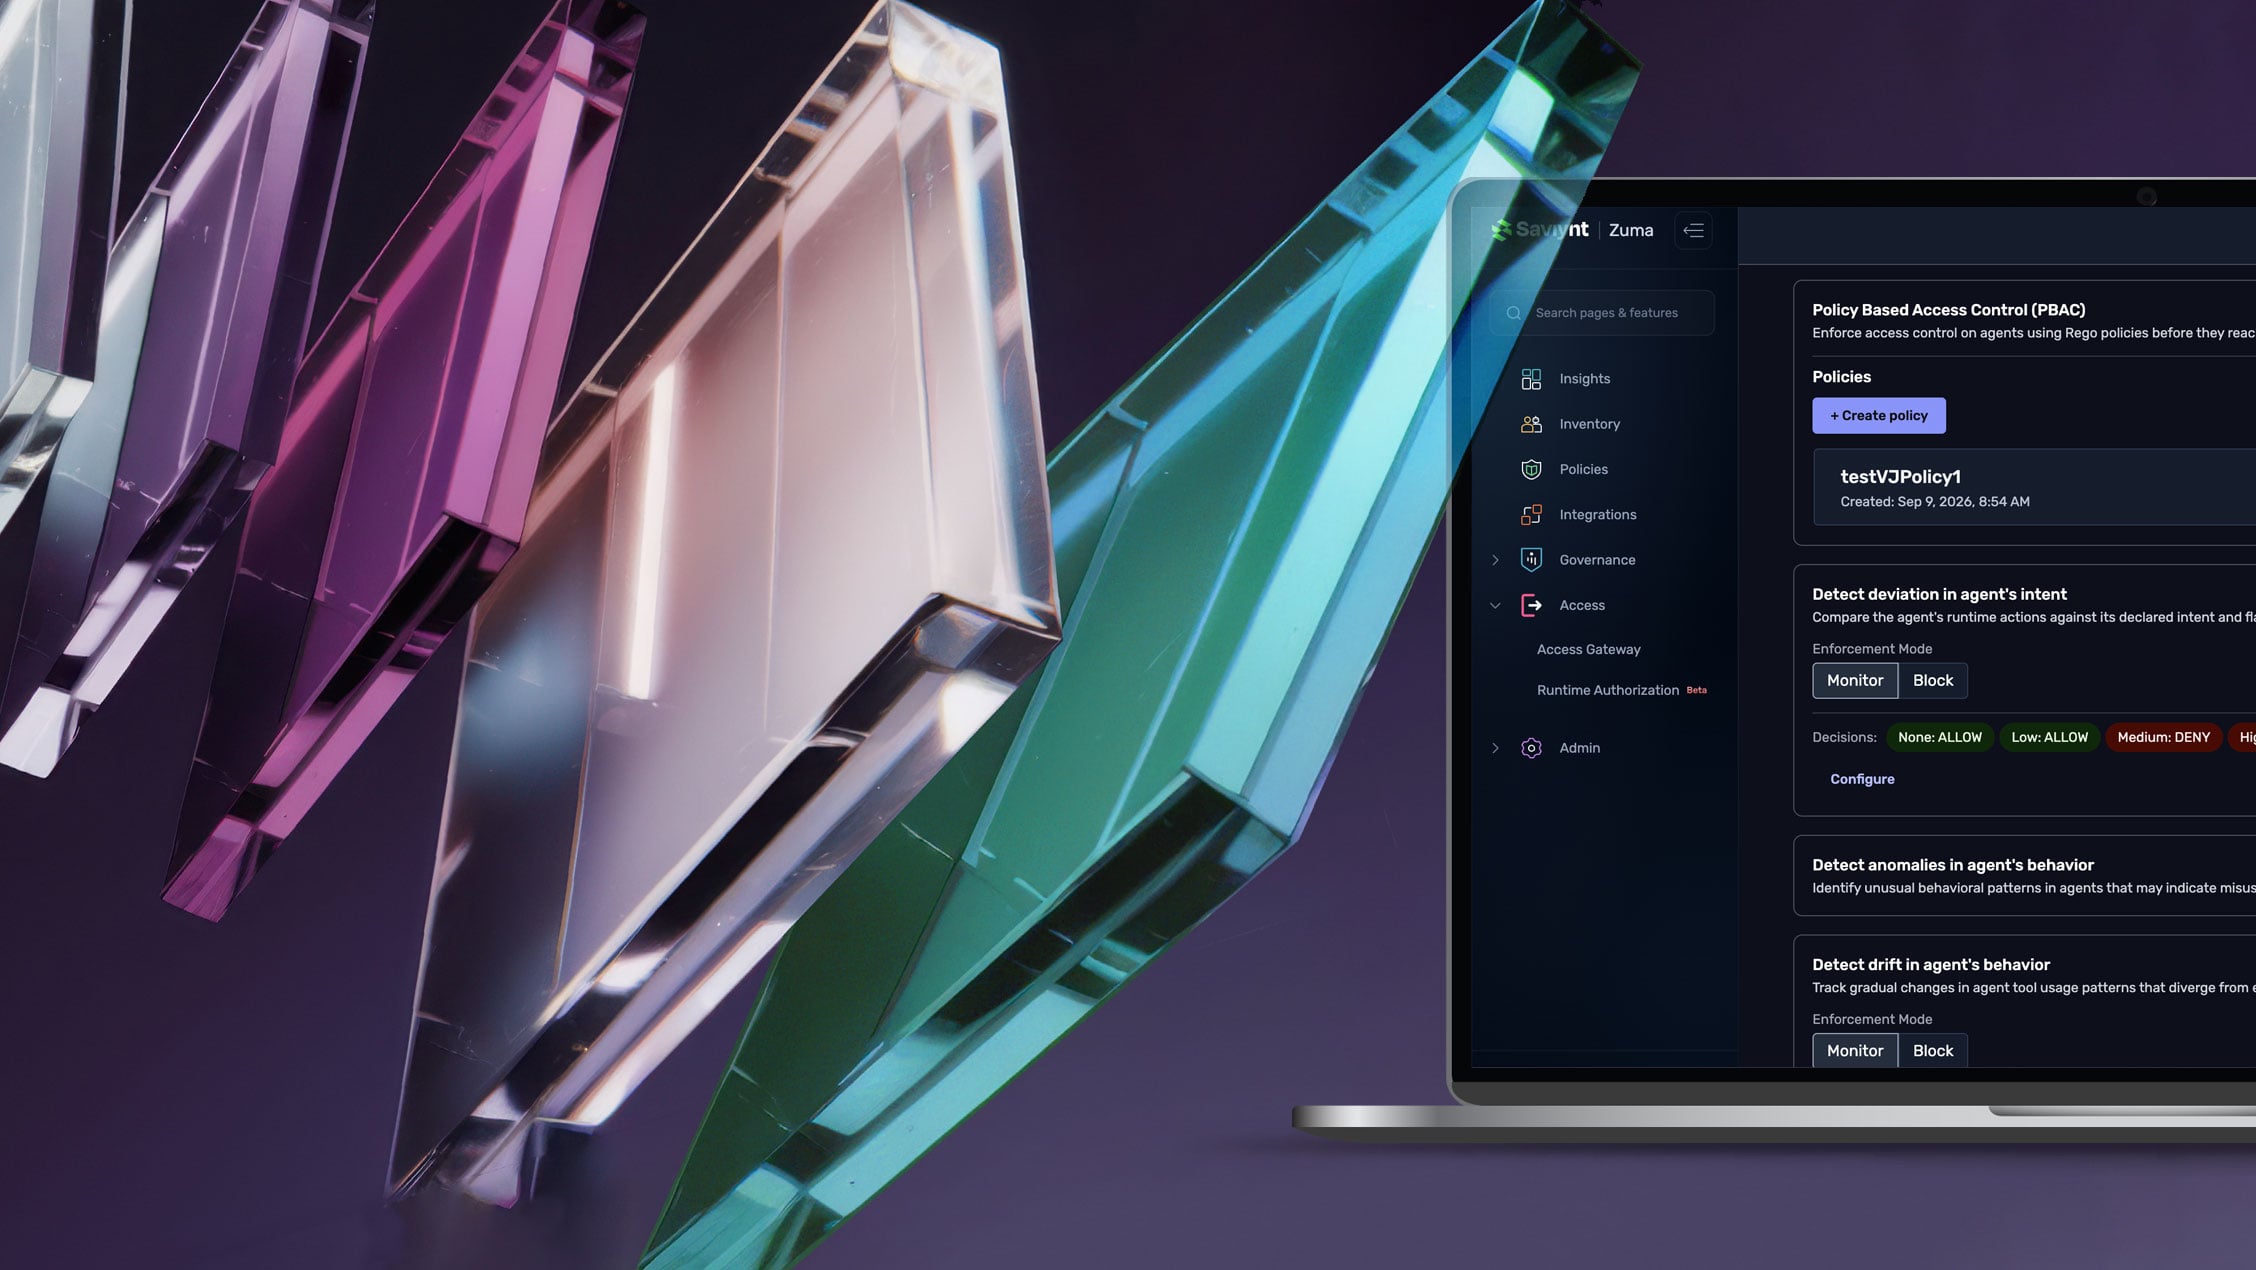
As AI agents begin to take action independently, Saviynt ensures both users and agents operate with tightly scoped permissions, dramatically reducing blast radius and audit risk.
AI license cost control
With centralized visibility and access certifications, organizations can reclaim unused or misassigned premium AI seats, keeping Claude and Kiro spend aligned with real usage.
Governing the entire AI access lifecycle
Saviynt IGA now governs the full lifecycle of AI tools from automated provisioning and entitlement mapping to continuous certification and cost optimization.
Stay tuned as we continue to deliver integrations with more AI platforms, and head over to our homepage to learn more about how Saviynt can help your organization govern the future of identity.