Access reviews (also called certifications or attestations) are one of the most important controls in an identity security program. They're how organizations catch access that's noncompliant or outlived its purpose before it becomes a breach or audit finding. They're also expensive: every review cycle pulls managers, application owners, and other highly paid leaders away from their actual jobs to certify who has access to what.
The high stakes of risk mitigation and compliance mandates make access reviews the control auditors ask about first, and also the one most likely to degrade into a rubber-stamping exercise when it isn't run well. Get it wrong, and you're burning leadership time without actually reducing risk; get it right, and you minimize the drag on the organization while walking into your next audit with a clean, defensible record. Here's a short list of ways organizations can get more value out of the time and resources they spend on reviews.
1. Understand that the core failure mode is certification fatigue
When reviewers face hundreds or thousands of line items, they get overwhelmed, decisions slow down, and reviewers start approving things they haven't actually examined. This is access review fatigue: the predictable result of asking managers or app owners to certify large volumes of access too often with too little context.
The fix: stop treating every review as "look at everything." Scale scope and frequency to risk and compliance needs instead of running the same exhaustive quarterly sweep regardless of what's changed.
2. Use risk scoring and recommendations to let AI prioritize the work
Use signals to separate access that's obviously fine from access that needs a real look. Saviynt's AI-powered Intelligence engine scores access risk using 14+ signals, including peer comparisons, SoD conflicts, out-of-band access, and prior certification history, giving reviewers a trust score, a plain-language explanation, and a recommendation based on pre-defined criteria and decision thresholds.
Organizations using capabilities like these report faster campaign completion, fewer steps per review, and higher revocation rates on access that genuinely didn't belong. Reviewers can focus on anomalies and outliers, improving decision effectiveness while reducing rubber-stamping due to decision fatigue.
3. Give reviewers context, not raw entitlement lists
Approvers can't review access well when all they see is a technical role name and a system ID. Business-friendly application, entitlement descriptions, and flagged exceptions give a non-technical manager what they need to make a real decision instead of guessing.
4. Fix the data before you fix the process
Access reviews are only as good as the data behind them. Before rolling out a better review process, the underlying platform needs accurate role definitions, entitlement descriptions, usage data, and risk classifications. Otherwise, you're just making a bad process faster. Pilot with a willing, motivated team rather than a big-bang rollout, and use early results to build momentum.
Data quality also depends on getting applications into the governance framework in the first place, and that's traditionally been the slowest part. Saviynt's Application Integration and Onboarding Agent uses agentic AI, LLM-powered configuration, and infrastructure-as-code to onboard connected, disconnected, and legacy applications alike, cutting onboarding from weeks to hours and without requiring deep application-specific expertise.
5. Let users certify their own access first
Empower individuals to review their permissions first, as they are best positioned to know if access is still required. Self-certification accelerates campaign completion by letting users quickly verify or report entitlements, while fostering accountability through explicit self-attestation. Consequently, this streamlines subsequent review stages for managers, executives, and application owners.
6. Route to the right reviewer, and make it easy for them
Reviewer assignment matters as much as review content:
- Multi-level review chains (e.g., manager first, then application or data owner) so no single reviewer is a single point of failure.
- Reassignment or delegation when the assigned reviewer isn't the right person.
A short training session before each campaign meaningfully improves review quality. Reviewers who don't understand why the review matters or what to look for will default to rubber-stamping, no matter how good the UI is.
7. Be careful with “approve all”
If your platform has a select-all-and-approve function, be thoughtful about it. It exists for admin convenience, but it's the single biggest enabler of rubber-stamping. Pair that with a hard rule: no bulk decisions on high-risk or privileged access, ever, no matter how the tool is configured.
Saviynt’s platform features AI-driven recommendations that suggest whether to retain or revoke entitlements. Organizations can use these insights to automate low-risk access decisions, saving approver bandwidth to focus on higher-risk permissions.
8. Close the loop, ensuring access actually changes
A certification isn't complete when someone clicks "revoke." Someone needs to confirm the campaign accurately reflects the intended access state. Access granted automatically through role membership rules can't be revoked by clicking revoke in the certification tool — the underlying membership criteria has to change, or the system will just reassign it. This gap, where the certification shows "revoked" but the downstream system was never updated, is exactly what auditors look for.
9. Extend governance beyond human identities
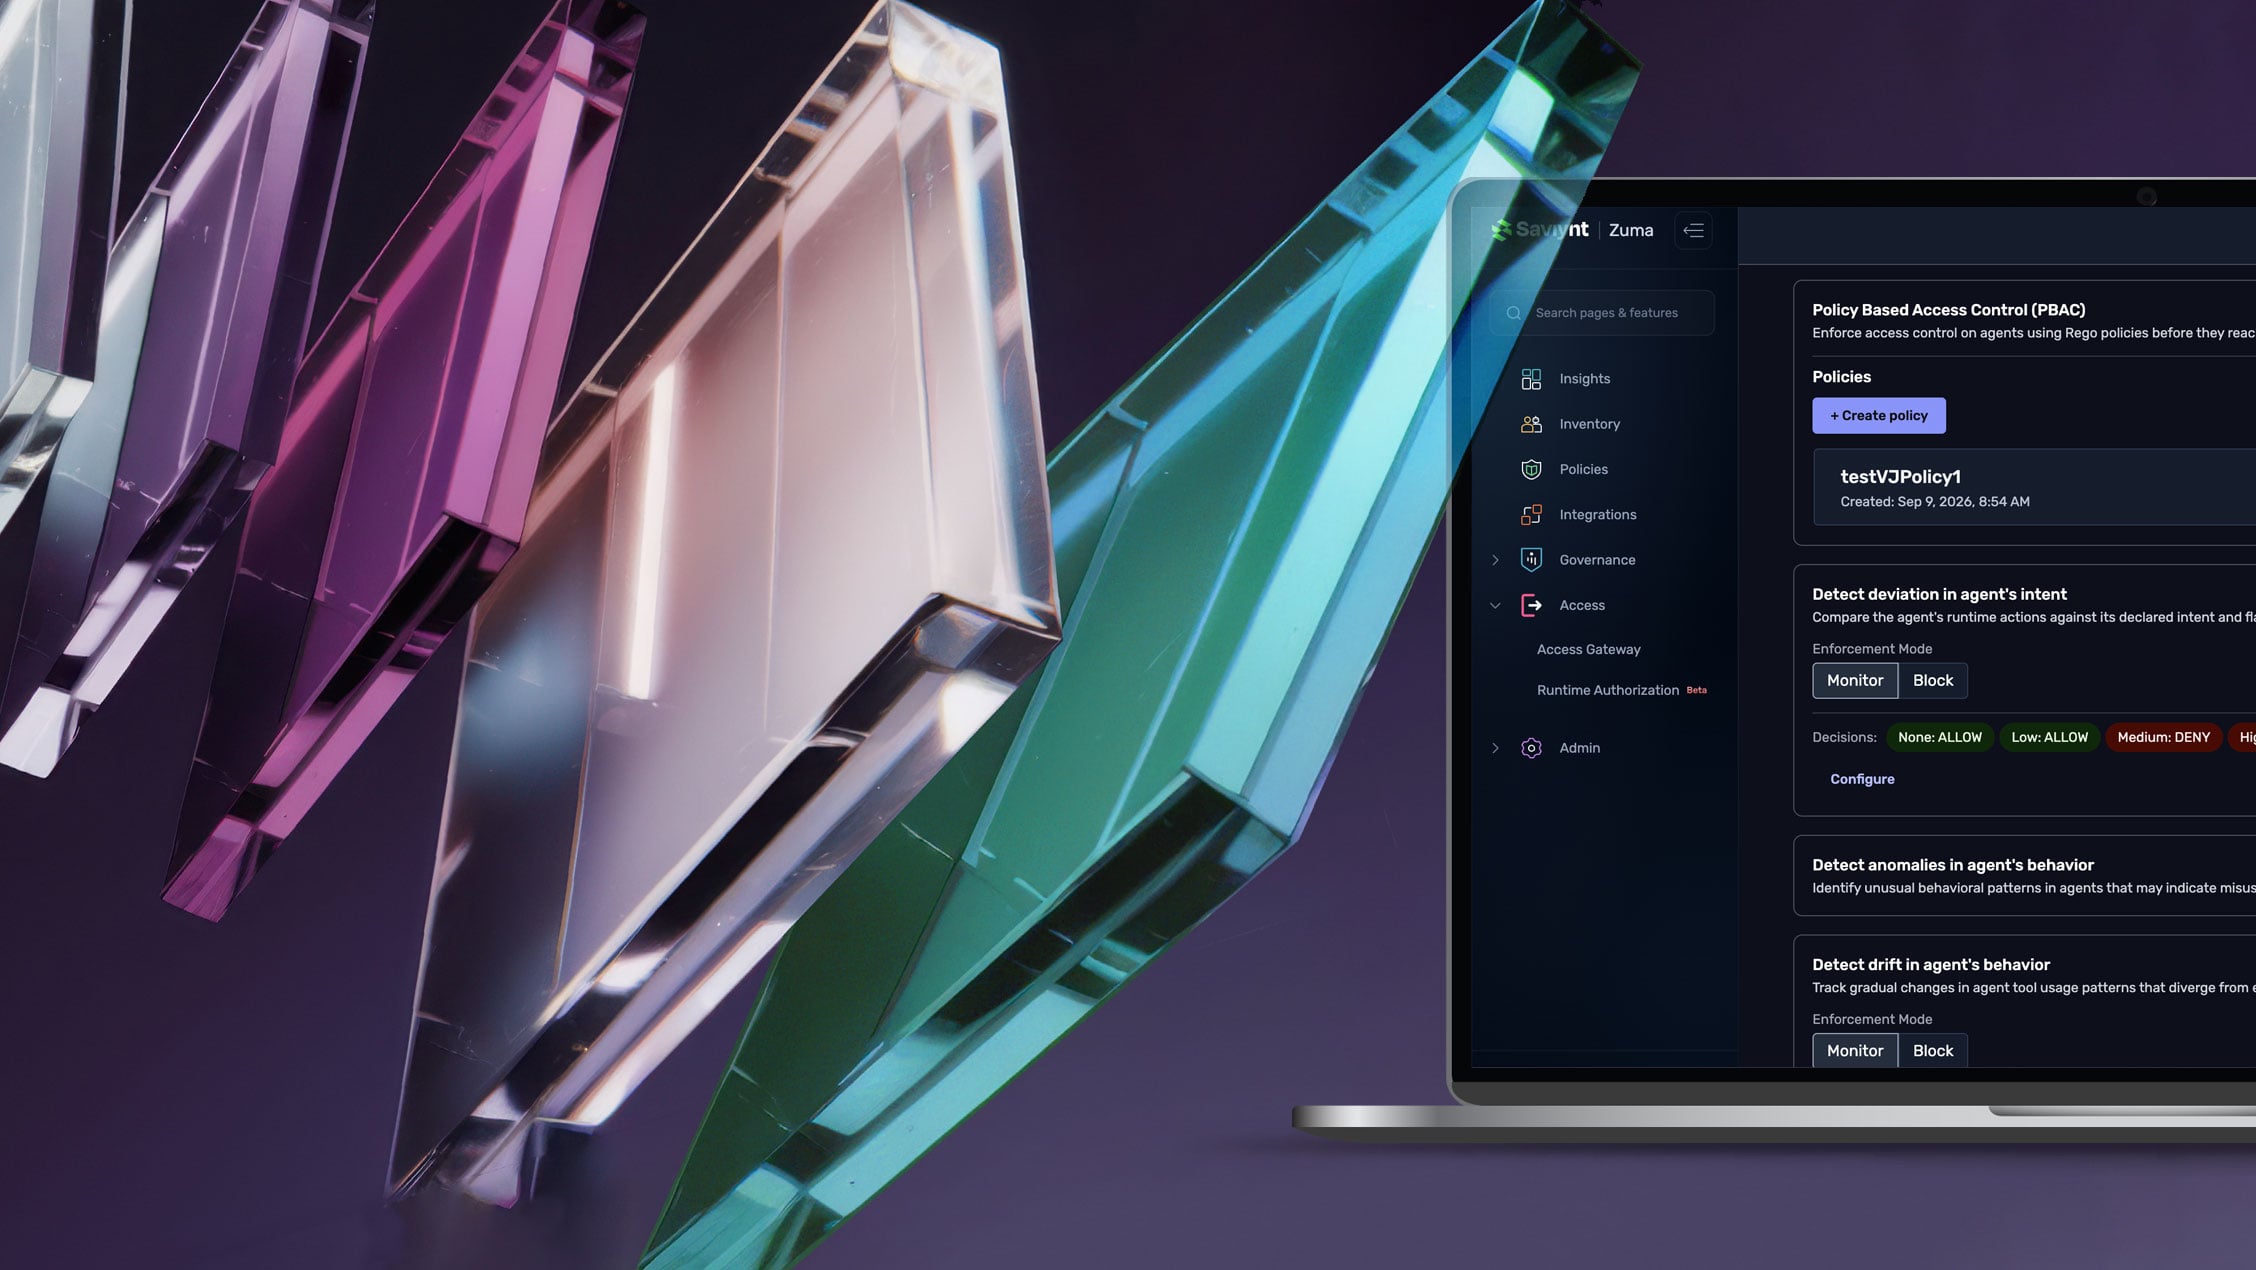
This is newer territory, but it's moving fast. Non-human identities, including service accounts, AI agents, and machine identities, now outnumber human ones in most enterprises, and they need the same ownership, periodic review, and lifecycle controls human access reviews have had for years. Saviynt's Zuma, an AI identity security platform, targets exactly this: ownership assignment, continuous access review, and audit trails for AI agents. If your program still treats "identity" as synonymous with "employee," this is the gap most likely to bite you in the next audit cycle.
10. Automate the overhead away, for reviewers and admins alike
Access reviews are overhead for almost everyone who touches them. Reviewers need an interface that's flexible enough to fit how they actually work, personalized to what they specifically own, and fast enough that a review doesn't turn into a half-day chore.
Many organizations are still running review cycles off manual spreadsheets that don't repeat cleanly from one cycle to the next. Admin teams end up tracking progress, chasing down reviewers, troubleshooting issues, remediating access, and collecting audit evidence all by hand. Saviynt's platform automates each step, makes the cycle repeatable, uses pre-launch analytics to catch problems before a campaign starts, and builds audit evidence collection into the process. The result is a cleaner audit cycle with less manual overhead and higher satisfaction from everyone who has to run it.
In summary, access reviews shouldn't force a choice between rubber-stamping and burning out your reviewers. Saviynt's identity security platform builds in the best practices covered here: risk-based scoring, context reviewers can actually use, controls that block bulk approvals, closed-loop revocation, and governance that covers non-human identities as well as people. Check out Saviynt to learn more or set up a demo and see how it applies to your environment.